What Does the DPDP Act Mean For Employers Hiring In India?
The DPDP Act and Rules introduce new data protection duties for employers hiring in India. Learn about employee consent, candidate data retention, EOR responsibilities, breach reporting, penalties, and key steps to prepare for the May 2027 compliance deadline.
What You Need to Know
The DPDP Act for employers comes down to one date and one exemption. The Digital Personal Data Protection Act, 2023 and its Rules apply to every digital employee and candidate record processed in India. But your duties as an employer, and penalties of up to ₹250 crore, begin on 13 May 2027.
Section 7(i) of the Act lets you process employee data for employment purposes without consent. So you don’t need a consent form for payroll, PF filings, appraisals, or misconduct inquiries.
That exemption stops at the employment door. Candidate data from people who never join sits mostly outside Section 7(i). Your deletion rule also has to respect a one-year floor under Rule 8(3).
And you are not in a legal vacuum before May 2027. Section 43A of the IT Act and the SPDI Rules, 2011 already cover salary accounts, medical records and biometric attendance.
Is the DPDP Act in force for employers yet?
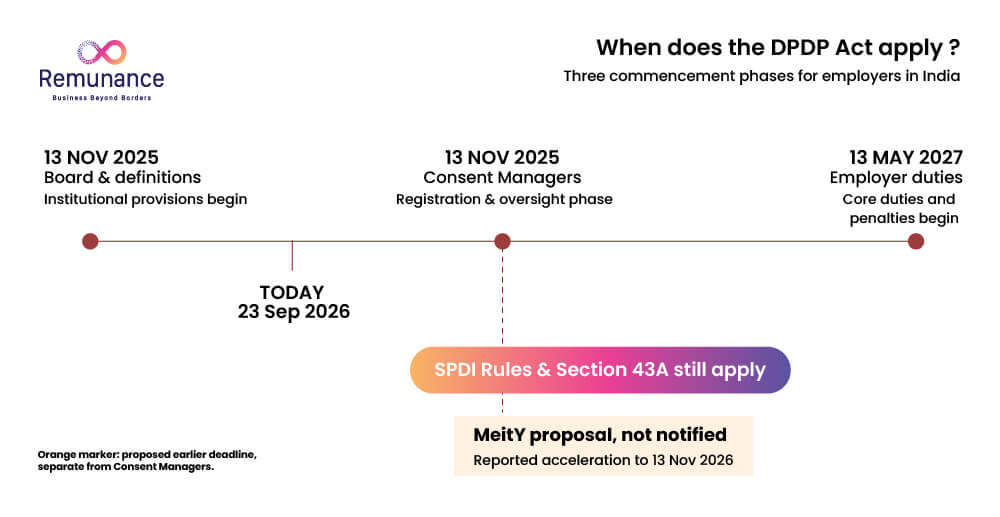
Partly. The definitions and the Board provisions have been in force since 13 November 2025, but your core employer duties start on 13 May 2027.
The Government used a staged commencement for the Act and the Rules. The Rules were notified as G.S.R. 846(E), and the PIB release on the DPDP Rules confirms the 18-month phased window.
What are the Three DPDP Commencement Dates?
There are three. Only the last one creates day-to-day duties for your HR team.
| Phase | Date | What starts | What it means for your India HR team |
| Phase 1 | 13 Nov 2025 | Definitions, the Data Protection Board, Rules 1, 2 and 17 to 21 | Nothing changes on employee files yet |
| Phase 2 | 13 Nov 2026 | Consent Manager provisions, Rule 4 | Relevant only if employees manage consent through a registered Consent Manager |
| Phase 3 | 13 May 2027 | Sections 3 to 17, the penalty provisions, Section 44(2), Rules 3 and 5 to 16 | Notice, security, breach, retention, rights, transfers and penalties all apply |
You will see 14 November 2025 in some sources. That is the date PIB announced the Rules, a day after the Gazette date. Plan around 13 May 2027.
Could the 13 May 2027 Deadline Move Earlier?
It could, so plan for the risk. In January 2026, MeitY proposed at a stakeholder meeting to cut the window from 18 months to 12, which would have pulled the date to 13 November 2026, as this analysis of the MeitY proposal sets out.
As of September 2026, no amending notification has appeared in the Gazette. The reports also point the shorter window at Significant Data Fiduciaries, such as large platforms and banks, rather than ordinary employers.
So treat 13 May 2027 as the legal date for your policies, vendor contracts and board papers. But finish your employee data map and breach runbook before 13 November 2026. Then a late amendment costs you nothing.
Is the Data Protection Board of India Actually Working?
It exists in law, but it had no Chairperson or Members as of August 2026. The Data Protection Board of India was established on 13 November 2025, and MeitY sought nominations for its posts in May 2026, as LiveLaw reported in August 2026.
That matters less than it sounds. Your duties don’t wait for the Board. What stays unknown is how the Board will set penalty levels, and nobody can predict that before its first cases.
Which Data Protection Rules Bind Your India Tam Before May 2027?
The IT Act, 2000 and the SPDI Rules, 2011 do. Section 44(2) of the DPDP Act omits Section 43A of the IT Act, but Section 44(2) itself only commences on 13 May 2027.
Until then, Section 43A and the SPDI Rules remain live law, which Legal500’s September 2026 analysis confirms. Most employer guides skip this. Yet it is the only general data protection regime anyone can hold you to today.
What counts as sensitive data in an HR file under the SPDI Rules?
Rule 3 of the SPDI Rules lists passwords, financial information, health data, medical records, sexual orientation and biometric information. A standard India employee file touches four of those.
-
- Salary account details you collect for payroll count as financial information.
- Health insurance enrolment and sick-leave certificates count as health data, and our guide to health insurance for employees in India shows how much of it flows to insurers.
- Biometric attendance from a fingerprint or face scanner counts as biometric information.
- Initial system passwords your IT team issues to new joiners count as passwords.
That covers most of a standard onboarding pack.
What do the SPDI Rules require you to do right now?
They require written consent before you collect sensitive data, and email or any electronic mode counts. Rule 5 also asks you to tell the person the purpose, the recipients, and who holds the data.
The same Rules expect a published privacy policy, a named grievance officer, and reasonable security practices. IS/ISO/IEC 27001 is the standard the Rules name. You also need consent before you share that data with a third party, unless a contract or a legal duty covers the disclosure.
Section 43A adds a remedy the DPDP Act lacks. An employee can claim compensation if your negligent security causes wrongful loss. The DPDP Act has no such route, and Section 34 sends its penalties to the Consolidated Fund of India. So after May 2027, your risk shifts from damages claims to Board penalties.
What happens to your SPDI consent forms on 13 May 2027?
They stop being the right basis for employment processing. From that date Section 7(i) covers payroll and benefits without consent, so don’t carry SPDI consent wording into your DPDP notices.
The reason is withdrawal. A person can withdraw DPDP consent at any time, and you must then stop processing. If payroll rests on consent, one withdrawal leaves you stuck. Keep the old forms as evidence of past compliance, and rewrite your employee privacy notice around Section 7(i) before May 2027.
Is Your India HR Team Ready for DPDP Compliance?
Review your current SPDI compliance, employee data consent forms, and privacy policies before the DPDP Act’s May 2027 deadline. Get expert support to prepare your HR processes.
Does the DPDP Act Apply To A Foreign Company Employing People In India?
Yes, wherever the processing happens in India. Section 3 covers processing within India, plus processing outside India connected with offering goods or services to people in India.
Your EOR’s payroll run in Pune, with its PF uploads, salary transfers and payslip emails, is processing within India in the plainest sense. So is your own subsidiary’s HR system. If you also sell to Indian customers, the extraterritorial limb reaches your parent company directly.
The grey area is a foreign parent that only employs people in India and sells nothing to Indian customers. Employing someone is not obviously offering them goods or services. No court or Board has ruled on this, so don’t build your policy on that gap.
Does your hiring model change your DPDP exposure?
Yes. It changes who decides why and how the data gets processed, and under the Act, that decision- not the job title on the contract- is what makes someone a data fiduciary. The three common models split the load like this.
| Hiring model | Legal employer | Data fiduciary for payroll and statutory records | Your main DPDP job |
| Own subsidiary | Your Indian entity | Your Indian entity | Every duty, in-house |
| Employer of record (EOR) | The EOR | The EOR | Work data you control, plus vendor oversight |
| Independent contractors | None | Each party for its own records | Contract data, plus misclassification risk |
If you are still choosing a route, weigh data duties with cost in our EOR or subsidiary comparison. An EOR also lets you hire in India without an entity and keeps payroll records with the legal employer.
Contractors need a different basis. Section 7(i) covers employment only, so you rely on Section 7(a) for data a contractor gives you to perform the contract. A contractor of record can run contracts and payments. But watch employee misclassification, because a mislabelled contractor drags your data basis down with the contract.
Does the Act cover your India GCC when it processes global employee data?
Mostly not, because of Section 17(1)(d). When an India-based entity processes data of people outside India under a contract with a foreign party, most of the Act switches off.
Two duties survive. Section 8(1) keeps the fiduciary accountable, and Section 8(5) still demands reasonable security safeguards. So a GCC in India running HR shared services for US staff needs strong security, but not DPDP notices for those US employees.
Your GCC’s own India employees stay fully covered, whether you employ them through a subsidiary or build the GCC through an EOR model.
Do You Need Consent To Process Employee Data Under the DPDP Act?
Usually not. Section 7(i) treats processing “for the purposes of employment” as a legitimate use, so core HR work needs no consent form.
The clause also covers safeguarding you from loss or liability, such as corporate espionage or leaked trade secrets. It extends to any service or benefit an employee asks you for.
What does Section 7(i) cover day to day?
It covers the processing required to run an India team, from the day an offer letter goes out to the day the final settlement clears. Think payroll, PF and ESI enrolment, leave, appraisals, promotions, disciplinary inquiries and IT access controls.
Statutory filings get a second basis too. Section 7(d) covers processing to meet a legal duty to disclose information to the State. PF returns to the EPFO, ESI contributions and TDS filings fit that description. Our guide to payroll compliance in India lists the filings involved.
When do you still need an employee’s consent?
You need it once the purpose moves outside employment. Using an employee’s photo in an ad campaign, passing their details to a partner, or reusing HR records to train a product model all fall outside Section 7(i).
For those, Section 5 and Rule 3 require a standalone notice in clear language. Section 5(3) also gives the person the option to read it in English or any Eighth Schedule language. Section 6 then requires consent that is free, specific, informed and unambiguous, and easy to withdraw.
Does the employment exemption switch off your other duties?
No. Section 7(i) removes the need for consent and nothing more. Security safeguards, breach reporting, accuracy, retention limits and grievance handling all still apply.
Accuracy deserves your attention. Section 8(3) requires complete, accurate and consistent data wherever you use it to make a decision about the person. Appraisal scores that feed a promotion or a termination of employment sit squarely inside that duty.
What if you hire interns or apprentices under 18?
Treat them as a special case. Section 9 requires verifiable consent from a parent before you process a child’s personal data, and the Act treats anyone under 18 as a child.
Section 9 carries no employment carve-out. The exemptions in the Rules center on settings such as schools, clinics and childcare. So if you run an apprenticeship scheme for 17-year-olds, ask counsel to confirm the parental consent flow before you onboard.
How Does The DPDP Act Change Recruitment And Candidate Data?
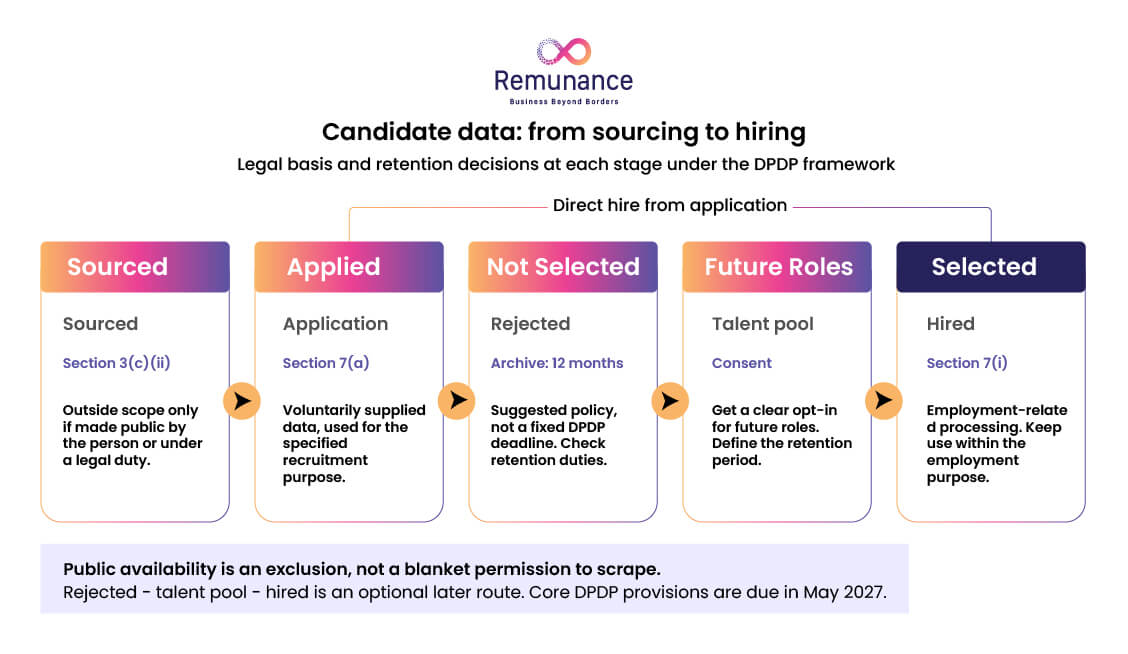
It changes more than employee data, because candidates aren’t employees yet. The cleanest basis for an application is Section 7(a), which covers data a person voluntarily gives you for a specified purpose.
Suppose a developer applies for your Pune backend role. They have given you their CV for that role. You can use it for that hiring decision without a consent form, unless they tell you they object.
Some advisers read Section 7(i) widely enough to cover recruitment. That reading is untested, so design around Section 7(a) and keep Section 7(i) as a fallback.
The moment you want the CV for another role, a talent pool, or an AI model, the purpose changes. That new purpose needs notice and consent.
Can you source candidates from LinkedIn and job boards?
Partly. Section 3(c)(ii) excludes personal data that the person made publicly available, so a profile someone published openly arguably sits outside the Act.
That exclusion is narrow. Read it tightly. A CV database you license from a job portal is not data the candidate made public. They shared it with the portal on the portal’s terms. And once you add interview notes to a sourced profile, you create new data that the exclusion doesn’t reach.
So give sourced candidates a short notice at first contact, in the same message where you pitch the role. Then ask before you keep them beyond the role you called about.
How long can you keep a rejected candidate’s data?
For at least one year, and not much longer without a reason. From 13 May 2027, Rule 8(3) requires every data fiduciary to retain personal data, traffic data and processing logs for at least a year from the processing.
That floor collides with the six-month auto-delete many recruiting guides recommend. SS Rana’s review of the final Rules shows the duty reaches data your processors hold too, such as a hosted ATS.
Let’s say a candidate applies on 1 June 2027 and you reject them on 15 July 2027. Archive the file away from your recruiters until at least 15 July 2028. The Seventh Schedule limits that year to State requests and similar purposes, so don’t mine the archive for your next requisition. Then delete it, unless the candidate joined your talent pool with consent. Twelve months, not six.
Do referrals, background checks and AI screening need separate handling?
Yes. Each needs its own treatment.
-
- Referrals: Your employee hands you a friend’s details, so the friend never voluntarily provided anything to you. Send the referred person a notice at first contact.
- Background checks: A verification firm that runs its own database and methods may act as a data fiduciary in its own right. Your contract should state which role it plays.
- AI screening: The DPDP Act sets no explainability duty for algorithms. But the Section 8(3) accuracy duty applies when a score drives a hiring decision, and our view on generative AI in HR covers the wider risks.
If an agency sources for you, agree the roles before the first CV arrives. Our guide to finding a recruitment partner in India covers the commercial side of that choice.
Remunance Employer of Record
Make Your Recruitment Process DPDP-Ready
Protect candidate data at every hiring stage, from CV collection and background checks to AI screening and talent pool retention. Get expert support to build a compliant hiring process in India.
Talk to Our Experts
Who Is The Data Fiduciary When You Employ Through An EOR?
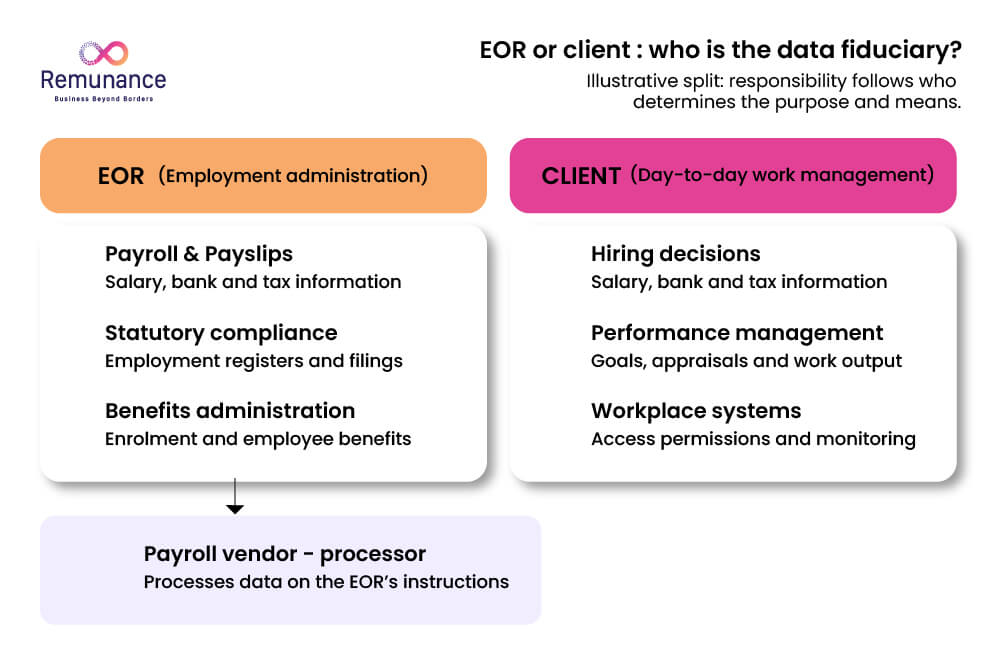
You both are, for different data. A data fiduciary is whoever decides the purpose and means of processing, alone or with others. So the answer follows the decision, not the label in your contract.
| Processing activity | Who decides purpose and means | Likely DPDP role |
| Payroll, TDS, PF and ESI filings | The EOR, as legal employer | EOR is data fiduciary |
| Employment contracts and statutory registers | The EOR | EOR is data fiduciary |
| Work allocation, goals and code reviews | You, the client | You are data fiduciary |
| Access to your laptops, email and SaaS tools | You, the client | You are data fiduciary |
| Sourcing and interviews you run yourself | You, the client | You are data fiduciary |
| Payroll software the EOR uses | The EOR instructs the vendor | Vendor is data processor |
Section 8(1) then closes the escape hatch. A fiduciary stays responsible for processing done on its behalf “irrespective of any agreement to the contrary”. A clause calling your EOR the sole controller moves no liability for data you decide on.
What should your EOR contract say about employee data?
It should allocate roles by activity and put breach and retention duties in writing. Check for six terms when you choose an employer of record.
-
- A role schedule like the table above, signed by both sides.
- Breach notice to you within a fixed number of hours, well inside the 72-hour Board deadline.
- A list of sub-processors and the countries where they store data.
- Retention periods tied to the labour codes and Rule 8(3).
- Your audit right, or a recent third-party security report.
- Data return and deletion steps if you switch EOR providers or move from a subsidiary to an EOR.
What Will You Have to Do Once Employer Duties Start on 13 May 2027?
Six things, and you probably run a rough version of most already. None of them is exotic. They come from Section 8 of the Act and Rules 6 to 9 and 14.
What security safeguards does Rule 6 require?
Rule 6 sets a floor, not a menu. You need encryption, masking, obfuscation, or tokenization, plus access controls on the systems holding the data.
You also need logging and monitoring that can detect and investigate unauthorized access, backups, and one year of log retention. Every processor contract must carry a security clause. Then add appropriate technical and organizational measures on top.
Test the logging line first. Ask each HR, payroll, and ATS vendor how long it keeps access logs, and get a one-year setting in writing before you renew the contract.
Remote teams widen the surface. Home networks and personal devices sit inside the same safeguard, so set device rules in your remote work strategy. If you monitor employee devices for security, tie the monitoring to a stated purpose and tell your team what you log.
How fast must you report an employee data breach?
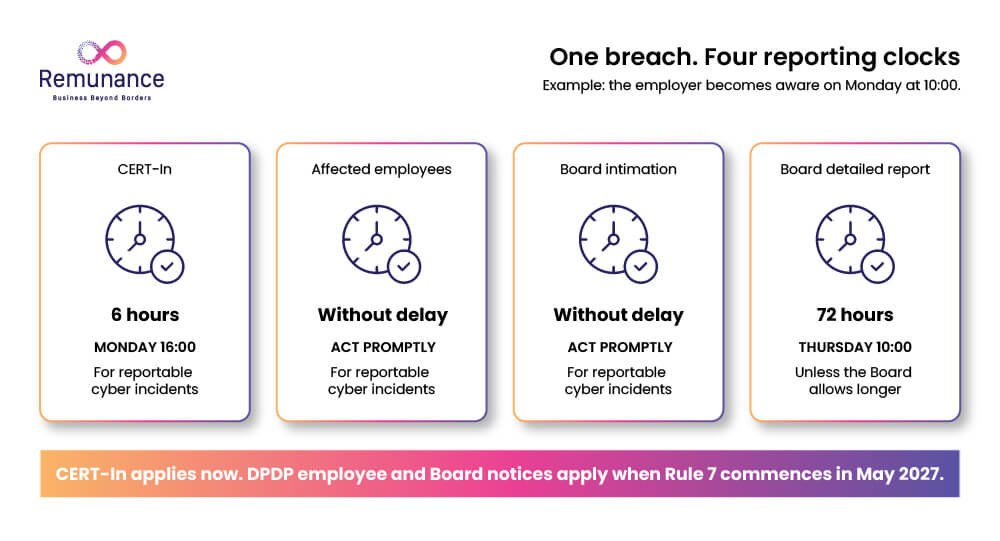
Without delay to affected employees and to the Board, then in detail to the Board within 72 hours. Rule 7 runs three clocks, and a fourth already runs today. Plan for all four.
Suppose your payroll processor finds at 10:00 on a Monday that it emailed a salary register for 240 India employees to an outside address. From the moment you become aware:
-
- Clock 1: Tell all 240 employees without delay, in plain language, with the likely impact and the steps they can take.
- Clock 2: Intimate the Board without delay, with the nature, extent, timing, location and likely impact of the breach.
- Clock 3: File the detailed report with the Board by 10:00 on Thursday, unless the Board grants more time on a written request.
- Clock 4: Report the incident to CERT-In within six hours. The CERT-In Directions of April 2022 already require this for data breaches and leaks.
Your DPDP clock runs from your own awareness. A processor that sits on the news for two days burns your window, which is why the breach term in your EOR contract matters.
How do the one-year log floor and the five-year register rule fit together?
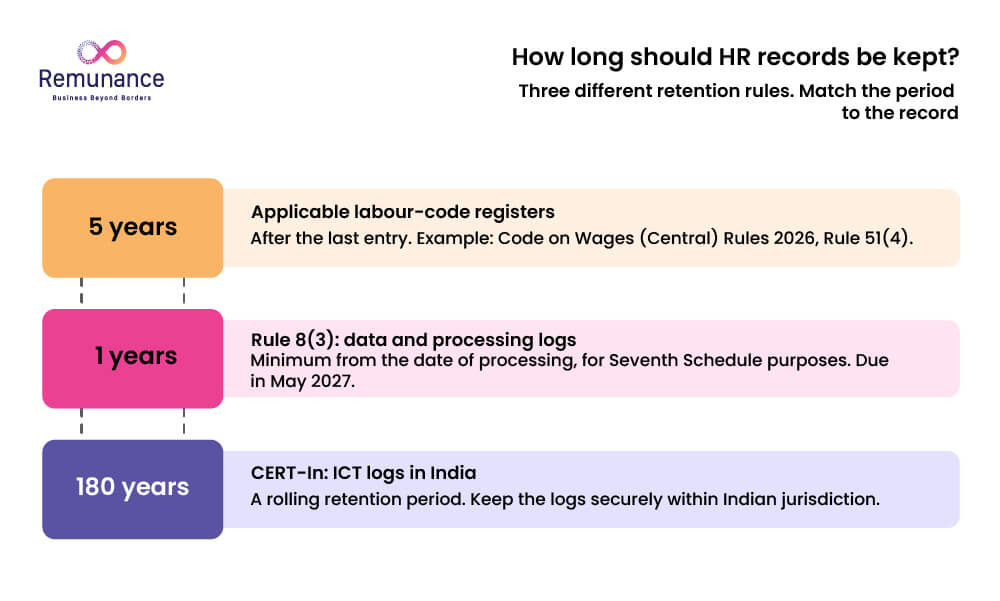
They stack. Rule 8(3) sets a one-year minimum for personal data and logs, and other laws can demand longer. For most employee records, the labour codes do.
| Record | Minimum retention | Source |
| Employee register, wage, overtime and deductions registers | 5 years after the last entry | Code on Wages (Central) Rules, 2026, Rule 51(4) |
| Social security registers | 5 calendar years from the last entry | Code on Social Security (Central) Rules, 2026 |
| Personal data, traffic data and processing logs | At least 1 year from processing, from 13 May 2027 | DPDP Rules, Rule 8(3) |
| ICT system logs | Rolling 180 days, kept in India | CERT-In Directions, April 2022 |
| PF and tax records | As the EPF scheme and income-tax law require | Confirm with your payroll provider |
| Rejected candidate files | At least 1 year, then erase unless consented | Rule 8(3) with Section 8(7) |
The Centre notified the Code on Wages (Central) Rules, 2026 on 8 May 2026, and Rule 51(4) sets the five-year period. Our guide to labour laws in India explains what else changed when the four labour codes took effect on 21 November 2025.
So an exit does not trigger deletion. At offboarding, you cut access and active use, and your retention clock starts.
Who must answer employee data questions and grievances?
You must publish a contact person and resolve grievances within 90 days. Rule 9 asks you to publish the business contact of someone who can answer questions about your processing, and Rule 14 sets the 90-day outer limit.
ELP’s note on the final Rules flags that the scope of the 90-day window is unclear, so aim well inside it. A formal Data Protection Officer is mandatory only for Significant Data Fiduciaries that the Government notifies.
Can You Transfer Indian Employee Data to Your Headquarters Abroad?
Yes. Section 16 works as a negative list, so a cross-border data transfer is allowed unless the Government notifies a country as restricted. Section 16 itself commences on 13 May 2027, and no country had been notified at the time of writing.
Sector rules still apply on top of the negative list. Section 16(2) preserves any Indian law that sets a higher bar, so banking and payments teams should check their regulator’s localization rules first. The January 2026 proposal also floated earlier transfer limits for Significant Data Fiduciaries. Most employers won’t be designated, but watch for it.
What changes if your headquarters is in the EU or UK?
The friction runs the other way. India has no EU adequacy decision, as the European Commission’s adequacy list shows. Data your EU entity sends to India needs a GDPR transfer tool such as Standard Contractual Clauses.
Picture a German parent whose managers write appraisal notes on India staff in an EU-hosted HR suite. The notes then sync to your Indian EOR. The DPDP Act lets data leave India freely, but GDPR decides whether it can arrive. So your EOR contract may need SCCs alongside the DPDP role schedule. UK GDPR works the same way, with the UK’s own transfer tools.
What Penalties Can an Employer Face Under the DPDP Act?
Up to ₹250 crore for failure to maintain reasonable security safeguards, with lower ceilings for other breaches. The Board fixes the actual amount after an inquiry.
| Breach | Maximum penalty |
| Failure to take reasonable security safeguards, Section 8(5) | ₹250 crore |
| Failure to notify a breach to the Board or affected people, Section 8(6) | ₹200 crore |
| Breach of children’s data duties, Section 9 | ₹200 crore |
| Breach of Significant Data Fiduciary duties, Section 10 | ₹150 crore |
| Any other breach of the Act or Rules | ₹50 crore |
| Breach of a Data Principal’s own duties, Section 15 | ₹10,000 |
At ₹88 to the dollar, the top line comes to about US$28 million. Section 33 asks the Board to weigh the nature, gravity and duration of the breach, the type of data, any repetition and your mitigation.
Rule 19 gives the Board six months to finish an inquiry, extendable three months at a time, as Cyril Amarchand Mangaldas’s client alert notes. Appeals go to the Telecom Disputes Settlement and Appellate Tribunal.
What would a penalty look like in a real HR incident?
Take the payroll email from the breach section. If the register sat unencrypted with open access, the Section 8(5) line applies, up to ₹250 crore. If you then stayed quiet, Section 8(6) adds a separate ceiling of up to ₹200 crore.
The first exposure depends on your systems. The second depends only on whether your team follows a runbook. Hence, a tested breach runbook is the cheapest control on this list.
What Should Your DPDP Compliance Checklist for India HR Data Include?
Ten tasks, ordered so each one makes the next cheaper. The dates assume the MeitY proposal could still pull the deadline forward, so the early tasks land before 13 November 2026.
| # | Task | Owner | Finish by |
| 1 | Map every system holding India employee and candidate data | HR ops and IT | 31 Oct 2026 |
| 2 | Tag each data category with its basis: 7(i), 7(d), 7(a) or consent | HR and counsel | 13 Nov 2026 |
| 3 | Collect SPDI written consent for bank, health and biometric data | HR ops | Ongoing to 13 May 2027 |
| 4 | Set log retention to at least one year across HR, payroll and ATS tools | IT | 31 Dec 2026 |
| 5 | Replace six-month candidate auto-delete with a 12-month archive rule | TA ops | 31 Dec 2026 |
| 6 | Write a breach runbook with the three DPDP clocks and CERT-In’s six hours | IT security | 31 Jan 2027 |
| 7 | Sign a role schedule and breach terms with your EOR and vendors | Legal and procurement | 28 Feb 2027 |
| 8 | Publish a contact person and a grievance route inside 90 days | HR | 31 Mar 2027 |
| 9 | Issue a new employee privacy notice built on Section 7(i) | HR | 30 Apr 2027 |
| 10 | Rehearse one breach and one erasure request end to end | HR and IT | Before 13 May 2027 |
Then send five questions to your India provider in writing:
-
- Which processing do you treat yourself as the data fiduciary for?
- Where do you store our employee data, and which sub-processors touch it?
- How many hours after discovering a breach will you tell us?
- How long do you keep records after exit, and under which law?
- Who is your published contact person for data questions?
Treat a vague answer on question one as a red flag, because role allocation decides who carries each duty after an incident. For the wider list, run your provider through our EOR compliance checklist.
How Does Remunance Help You Handle India Employee Data Under the DPDP Act?
As your employer of record, Remunance becomes the legal employer of your India team. So payroll, statutory filings and employment records sit with us, and so does the fiduciary duty for them.
-
- Onboarding: We collect what Indian payroll and filings need, as our employee onboarding process shows.
- Payroll and filings: We run payroll, PF, ESI and TDS as the legal employer, so you don’t have to work out how to pay employees in India yourself.
- Benefits data: We administer the employee benefits in India your team receives, including the insurer data flows.
- Devices: Our IT infrastructure support for EOR teams covers the laptops and access your India team uses.
- Exits: We handle final settlements and keep records for the periods the labour codes set.
Comparing providers first? Our list of the best EOR service providers in India sets out who does what.
Remunance Employer of Record
Simplify Employee Data Compliance With Remunance
Manage India payroll, statutory filings, employee benefits, and employment records with Remunance as your EOR partner. Prepare your HR operations for DPDP compliance with clear responsibilities and reliable local support.
Talk to Our India Team Frequently Asked Questions (FAQs)
Does the DPDP Act apply to employee data?
Yes. Every digital or digitised record about an identifiable employee falls under the Act. Paper records you never digitise sit outside it, but few HR files stay paper-only.
When does the DPDP Act come into force for employers?
On 13 May 2027 for the substantive duties and penalties. That is 18 months after the Rules were notified on 13 November 2025, and a January 2026 proposal to cut it to 12 months had not been notified by September 2026.
Is there a DPDP Act 2025?
No. The statute is the Digital Personal Data Protection Act, 2023. The 2025 instrument is the DPDP Rules, 2025, which make the Act work in practice.
Do employers need employee consent under the DPDP Act?
Not for employment purposes. Section 7(i) covers payroll, benefits, performance management and protecting you from loss. You need consent only when you use employee data outside employment, such as in marketing.
Can an employee ask you to delete their data?
They can ask, but labour law often requires you to keep it. Registers under the Code on Wages (Central) Rules, 2026 must stay for five years after the last entry. Explain the legal basis, delete what no law requires, and respond within 90 days.
Do you need a Data Protection Officer?
Only if the Government notifies you as a Significant Data Fiduciary, and most employers won’t be. You still need a published contact person under Rule 9 who can answer questions about your processing.
Does the DPDP Act apply to candidates who never join?
Yes. Candidate data is personal data, and Section 7(i) may not cover it because no employment exists yet. Rely on Section 7(a) for the role they applied to, get consent for talent pools, and archive files for at least a year.
Is my EOR responsible for DPDP compliance, or am I?
Both of you, for different data. Your EOR is the fiduciary for payroll and statutory records it controls as the legal employer. You remain the fiduciary for work data and systems you control, and Section 8(1) bars you from contracting that out.
Related Posts

EOR Compliance Checklist: What You Need to Know Before You Hire

How to Choose the Best Employer of Record?

Labor Laws in India: An Essential Guide for Employers
How to Hire International Employees Without an Entity
How Remunance Effectively Manages Employee Onboarding